Overview of CGRC Course in Noida
Our CGRC course in Noida is designed to offer learners a detailed understanding of Governance, Risk, and Compliance (GRC) principles, covering risk assessment, regulatory obligations, governance frameworks, and organizational control systems. The program prepares participants for the globally recognized CGRC Certification, helping them pursue career growth in governance, compliance, auditing, and risk management fields. The curriculum demonstrates how contemporary GRC practices help businesses recognize emerging risks, fulfill compliance requirements, and develop efficient governance processes while aligning operational activities with regulatory standards and organizational objectives. Participants understand how effective governance and compliance strategies contribute to improved business performance, informed decision-making, and stronger risk management capabilities. Major subjects included in the CGRC course in Noida encompass risk assessment, compliance management, auditing practices, policy implementation, governance frameworks, and control monitoring. Learners also obtain practical knowledge of industry-oriented GRC tools and platforms frequently used by enterprises for addressing real-time governance, compliance, and risk-related challenges. Through structured learning and practical exposure, participants develop essential skills for managing organizational risks, supporting regulatory compliance, strengthening internal controls, and implementing effective governance strategies across diverse business environments. The training further enhances professional confidence for handling complex enterprise GRC responsibilities.
Additional Info
Major Roles and Duties of CGRC Professionals
- CGRC Analysts: Assesses organizational risks, examines security controls, and contributes to sound business decisions through comprehensive evaluation and reporting tasks.
- GRC Consultants: Provides specialized recommendations, develops compliance approaches, and establishes governance frameworks throughout different business functions and activities.
- Risk Management Specialists: Recognizes possible threats, creates risk mitigation plans, assesses weaknesses, and strengthens organizational resilience through proactive measures.
- IT Auditors: Examines cybersecurity controls, conducts audit reviews, creates supporting records, suggests corrective measures, and confirms adherence to applicable requirements.
- Compliance Officers: Monitors legal and regulatory obligations, organizes compliance documentation, administers policies, and prepares essential records for internal and external assessments.
- Governance Analysts: Supports the creation of governance structures, connects policies with organizational objectives, promotes responsibility, and enhances business efficiency.
Common Tools Covered in CGRC Training in Noida
- GRC Platforms and Tools: Simplifies governance activities, automates oversight tasks, identifies potential risks, increases transparency, and strengthens organizational control procedures.
- Risk Management Software: Facilitates risk identification, evaluation processes, mitigation preparation, data analysis, and comprehensive reporting to support better organizational decision-making.
- Compliance Tracking Systems: Organizes regulatory records, follows compliance changes, provides alerts, and helps organizations meet essential compliance responsibilities.
- Auditing and Reporting Tools: Supports audit reviews, documents findings, creates detailed reports, enhances openness, and promotes accountability throughout enterprise governance structures.
- Dashboard and Analytics Tools: Delivers graphical insights into performance metrics, risk situations, compliance status, and operational data to support effective strategic decisions.
- Policy Management Tools: Helps businesses develop, revise, distribute, and oversee policies while maintaining consistency, governance coordination, and regulatory adherence.
Core Skills You’ll Develop Through a CGRC Course in Noida
- CGRC Fundamentals: Builds knowledge of governance principles, compliance obligations, policy structures, and organizational control systems through hands-on instructional activities.
- Risk Assessment: Develops capabilities in recognizing cybersecurity threats, examining consequences, ranking risks, and implementing appropriate risk treatment methods.
- Compliance Management: Strengthens abilities in tracking regulations, organizing documentation, applying controls, and sustaining required organizational compliance levels.
- Auditing and Control Management: Covers audit techniques, control assessments, supervision methods, and review practices designed to reinforce effective governance operations.
- Integration Skills: Develops the ability to connect governance structures with business operations, increasing efficiency and streamlining organizational workflows.
- Analytical Thinking: Strengthens problem-solving capabilities by examining information, interpreting data, and creating practical solutions for organizational challenges.
Career Outlook for CGRC Professionals
- Strong Industry Demand: Organizations require qualified specialists to manage compliance obligations, business risks, governance structures, and cybersecurity responsibilities.
- Professional Growth Opportunities: CGRC specialists can progress toward senior and managerial roles with expanded responsibilities, and attractive professional development prospects.
- Increasing Risk and Compliance Significance: Expanding regulatory requirements are generating opportunities for professionals responsible for governance functions.
- Global Employment Opportunities: CGRC expertise enables specialists to participate in international assignments, and cross-border governance and compliance initiatives.
- Growing Cybersecurity and Governance Requirements: Organizations seek capable professionals who safeguard business resources, reinforce internal controls, and remain aligned with changing regulatory.
- Diverse Career Opportunities: CGRC capabilities can lead to professional paths across consulting, auditing, cybersecurity, financial services, governance, and enterprise risk management sectors.
Show More
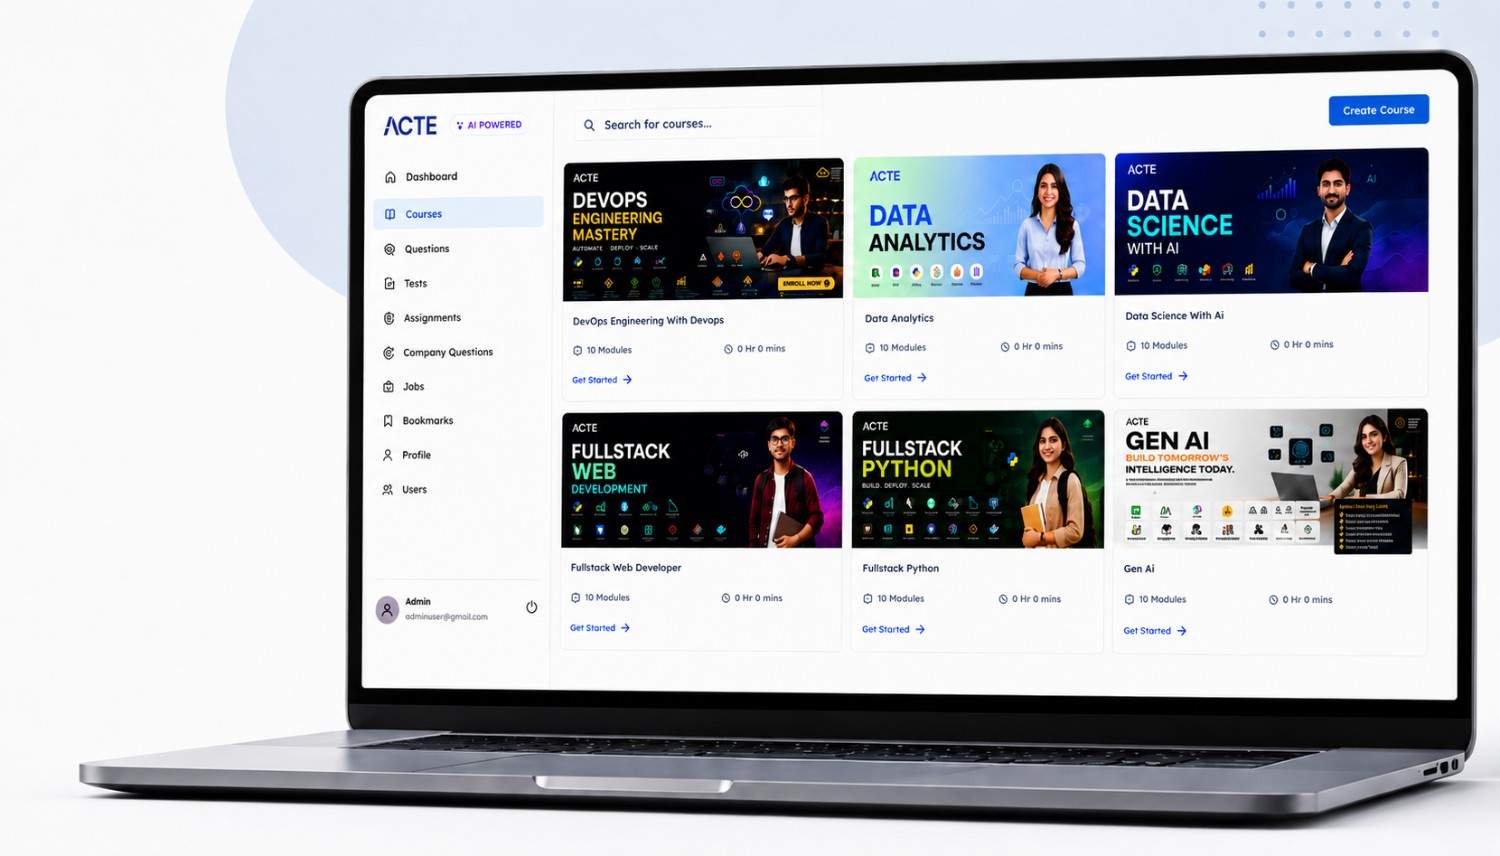
 LMS