Overview of CGRC Training in Kochi
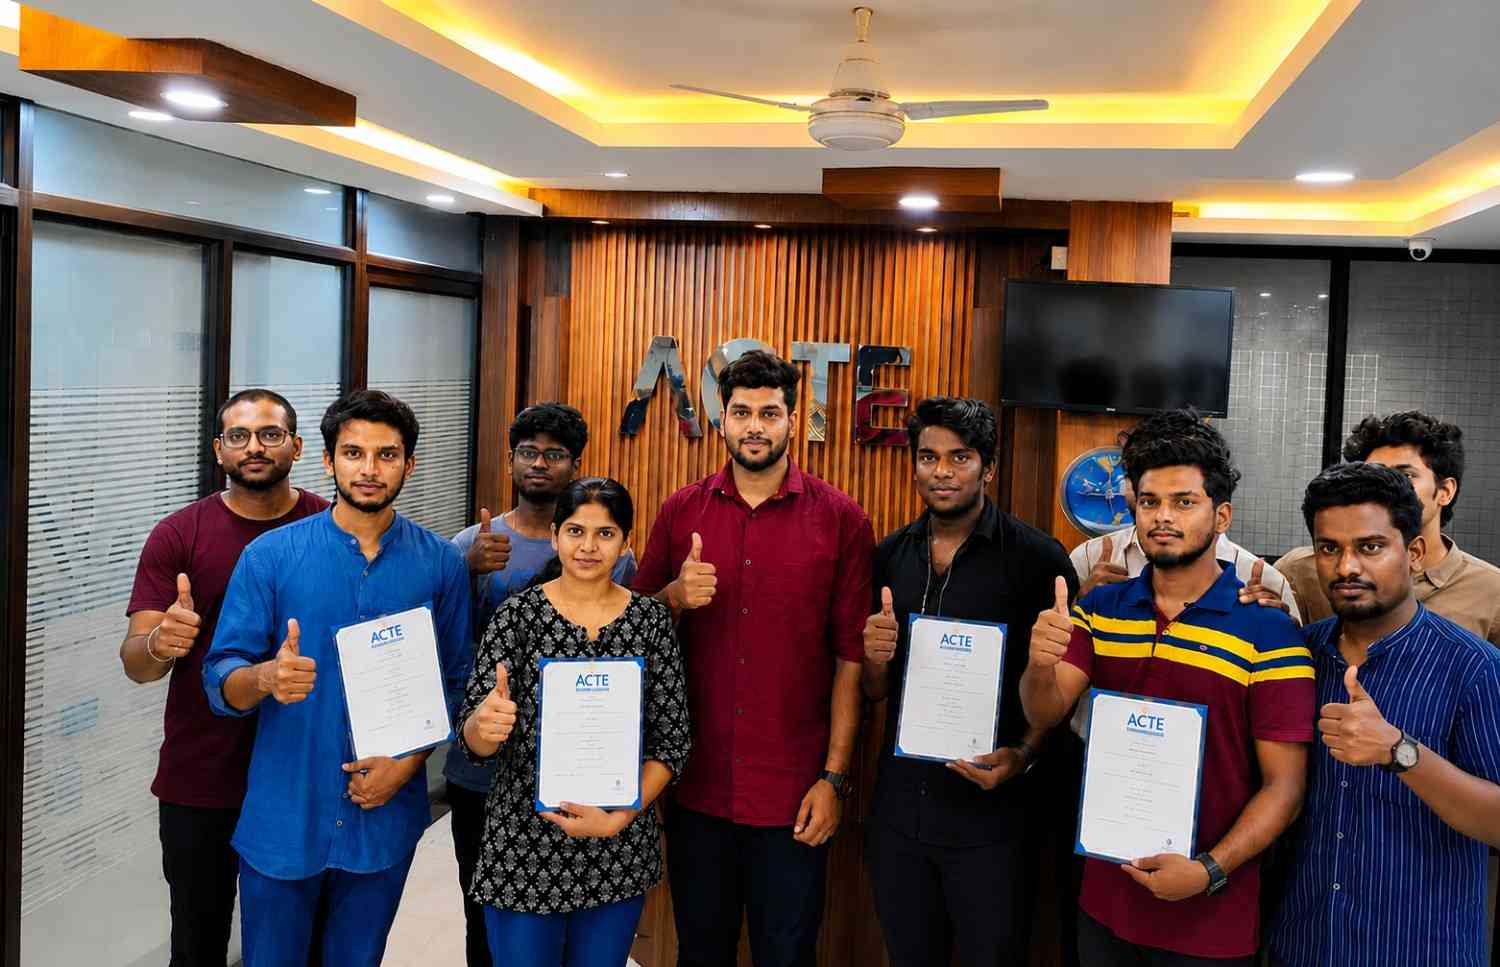
Our CGRC training in Kochiis designed to provide learners with a comprehensive understanding of Governance, Risk, and Compliance (GRC) principles, including risk evaluation, regulatory requirements, governance structures, and organizational control mechanisms. The program prepares participants for the globally recognized CGRC Certification, supporting career development in governance, compliance, auditing, cybersecurity, and risk management domains. The curriculum explains how modern GRC practices help organizations identify evolving threats, satisfy compliance obligations, and establish effective governance processes while aligning business operations with regulatory expectations and organizational goals. Participants learn how strong governance and compliance strategies improve operational efficiency, support informed decision-making, and strengthen enterprise risk management capabilities. Key areas covered in the CGRC training in Kochi include risk assessment, compliance management, audit procedures, policy implementation, governance frameworks, security controls, and continuous monitoring. Learners also gain practical exposure to current GRC tools and platforms used by organizations to address real-world governance, compliance, cybersecurity, and risk management challenges. Through structured instruction and practical activities, participants develop the skills required to assess organizational risks, support regulatory compliance, strengthen internal controls, and implement effective governance practices across diverse business environments. The training also builds professional confidence for managing complex enterprise GRC responsibilities.
Additional Information
Job Roles and Responsibilities of CGRC Placement
- GRC Analysts: Evaluates organizational risks, reviews security controls, monitors requirements, and supports informed business decisions through detailed assessment and reporting activities.
- GRC Consultants: Offers specialized guidance, develops compliance strategies, and establishes frameworks across business departments while supporting effective risk management practices.
- Risk Management Specialists: Identifies potential threats, develops mitigation strategies, evaluates vulnerabilities, and improves resilience through structured risk treatment activities.
- IT Auditors: Reviews cybersecurity controls, performs audit assessments, prepares documentation, recommends corrective actions, and verifies adherence to applicable regulatory requirements.
- Compliance Officers: Monitors regulatory obligations, compliance records, implements organizational policies, and prepares documentation for internal and external compliance reviews.
- Governance Analysts: Supports framework development, aligns policies with business objectives, promotes accountability, and improves processes through effective governance practices.
Current Tools and Technologies Covered in CGRC Training in Kochi
- ServiceNow GRC: Supports enterprise governance, risk, compliance workflows, policy management, risk assessments, issue tracking, and automated compliance activities across organizations.
- RSA Archer: Provides integrated governance, risk, and compliance capabilities for managing enterprise risks, regulatory requirements, controls, assessments, and compliance processes.
- IBM OpenPages: Enables organizations to manage risk, compliance, internal controls, regulatory requirements, audit activities, and governance processes through an integrated platform.
- Microsoft Purview: Supports data governance, compliance management, information protection, risk monitoring, requirements, and security-related activities across Microsoft environments.
- OneTrust: Provides solutions for privacy management, governance, compliance, risk assessment, regulatory tracking, and organizational policy management across enterprise environments.
- Power BI: Creates interactive dashboards, visualizes risk and compliance metrics, analyzes governance data, and supports reporting and management decision-making activities.
Core Skills You’ll Develop Through a CGRC Internship in Kochi
- CGRC Fundamentals: Develops knowledge of governance principles, compliance requirements, security policies, risk frameworks, and organizational control structures through practical learning activities.
- Risk Assessment: Builds expertise in identifying cybersecurity threats, evaluating business impact, prioritizing risks, and applying suitable risk treatment and mitigation strategies.
- Compliance Management: Strengthens skills in monitoring regulations, maintaining documentation, implementing controls, and supporting organizational compliance with applicable requirements.
- Auditing and Control Management: Develops knowledge of audit methodologies, control evaluations, evidence collection, monitoring procedures, and review practices for effective governance operations.
- Governance Integration: Builds the ability to align governance frameworks with business processes, improve operational efficiency, and coordinate compliance activities across organizational functions.
- Analytical Thinking: Enhances problem-solving by evaluating business information, interpreting risk data, identifying control gaps, and developing practical solutions for organizational challenges.
Career Outlook for CGRC Certification
- Strong Industry Demand: Organizations require skilled professionals to manage regulatory obligations, enterprise risks, governance frameworks, security controls, and compliance responsibilities.
- Professional Growth Opportunities: CGRC professionals can advance toward senior, specialist, and managerial positions with broader responsibilities and strong long-term development opportunities.
- Increasing Risk and Compliance Importance: Evolving regulations, cybersecurity threats, and requirements continue creating opportunities for qualified GRC professionals across industries.
- Global Employment Opportunities: CGRC expertise enables professionals to contribute to international projects, multinational organizations, and cross-border governance, risk, and compliance initiatives.
- Growing Cybersecurity and Governance Requirements: Businesses seek professionals who protect resources, strengthen internal controls, manage risks, and maintain alignment with changing regulations.
- Diverse Career Opportunities: CGRC skills can lead to career paths across GRC consulting, internal auditing, cybersecurity, financial services, compliance, and enterprise risk management sectors.
Show More
 LMS