Overview of CGRC Course in Ahmedabad
Our CGRC training is designed to equip learners with a thorough understanding of Governance, Risk, and Compliance (GRC) concepts, including risk assessment, regulatory obligations, governance frameworks, and organizational control processes. The CGRC Course in Ahmedabad prepares participants for the globally recognized CGRC Certification while supporting career development in cybersecurity governance, compliance, auditing, and risk management fields. The curriculum explains how effective GRC strategies help organizations identify emerging threats, meet regulatory responsibilities, establish structured governance processes, and align business activities with compliance standards and organizational objectives. Participants understand how efficient governance and compliance practices can improve operational performance, enable informed decision-making, and strengthen enterprise risk management capabilities. Key subjects covered in the CGRC Course in Ahmedabad include risk analysis, compliance administration, audit procedures, policy development, governance frameworks, security controls, and continuous monitoring. Learners also receive practical exposure to modern GRC tools and platforms used to address real-world governance, cybersecurity, compliance, and risk-related challenges. Through guided instruction, practical exercises, and the CGRC Training Internship, participants develop the ability to evaluate organizational risks, support regulatory compliance, strengthen internal controls, maintain governance standards, and implement effective GRC practices across different business environments. The training further enhances professional confidence and prepares learners to manage complex enterprise governance, risk, and compliance responsibilities.
Additional Information
Job Roles and Responsibilities of CGRC Course
- GRC Analysts: Assesses enterprise risks, examines security controls, tracks compliance needs, and supports business decisions through structured evaluations, analysis, and reporting.
- GRC Consultants: Provides expert advice, creates compliance strategies, and implements governance frameworks across departments while improving organizational risk management processes.
- Risk Management Specialists: Detects potential threats, assesses vulnerabilities, develops mitigation plans, and strengthens organizational resilience through systematic risk management practices.
- IT Auditors: Examines security controls, conducts technology audits, maintains assessment records, suggests improvements, and checks compliance with relevant regulatory requirements.
- Compliance Officers: Tracks regulatory obligations, manages compliance documentation, implements policies, and supports internal and external reviews to maintain organizational compliance.
- Governance Analysts: Build governance frameworks, align policies with business goals, promote accountability, and improve organizational processes through effective governance practices.
Current Tools and Technologies Covered in CGRC Training in Ahmedabad
- ServiceNow GRC: Helps organizations manage governance, risk, compliance workflows, policies, assessments, issues, and automated regulatory activities through a centralized platform.
- RSA Archer: Offers integrated GRC capabilities for identifying enterprise risks, managing controls, tracking regulations, conducting assessments, and streamlining compliance processes.
- IBM OpenPages: Provides an integrated solution for managing enterprise risks, compliance requirements, internal controls, audits, regulations, and governance activities efficiently.
- Microsoft Purview: Supports data governance, compliance, information protection, risk monitoring, regulatory management, and security activities across Microsoft-based business environments.
- OneTrust: Enables organizations to manage privacy, governance, compliance, risk assessments, regulatory requirements, and internal policies through centralized enterprise solutions.
- Power BI: Helps create visual dashboards, analyze governance and compliance information, track risk indicators, and generate reports that support informed business decisions.
Core Skills You’ll Develop Through a CGRC Training in Ahmedabad
- CGRC Fundamentals: Gain practical knowledge of governance, compliance, security policies, risk frameworks, and organizational controls through structured and real-world learning activities.
- Risk Assessment: Develop skills to identify cybersecurity threats, assess business impact, prioritize risks, and implement effective risk treatment and mitigation strategies.
- Compliance Management: Build expertise in tracking regulations, maintaining compliance records, implementing controls, and supporting organizations in meeting applicable requirements.
- Auditing and Control Management: Learn audit methods, control assessment, evidence gathering, monitoring techniques, and review practices to support effective governance and compliance.
- Governance Integration: Learn to align governance frameworks with business processes, enhance operational efficiency, and coordinate compliance activities across organizational functions.
- Analytical Thinking: Strengthen problem-solving skills by analyzing business data, assessing risks, identifying control gaps, and developing practical solutions to organizational challenges.
Career Outlook for CGRC Trainig
- Strong Industry Demand: Build expertise in governance, risk, and compliance as organizations seek skilled professionals to manage regulations, security controls, and enterprise risks.
- Career Advancement: Develop CGRC expertise to pursue senior, specialist, and managerial roles with greater responsibilities, leadership opportunities, and long-term career growth.
- Rising GRC Opportunities: Growing cyber threats, changing regulations, and compliance needs are increasing demand for skilled governance, risk, and compliance professionals.
- Global Career Prospects: Apply CGRC skills across international projects and multinational organizations, supporting global governance, risk management, security, and compliance initiatives.
- Growing Governance Needs: Help organizations strengthen security controls, protect critical resources, manage enterprise risks, and maintain compliance with evolving regulatory requirements.
- Diverse Career Paths: Explore opportunities in GRC consulting, internal auditing, cybersecurity, compliance, financial services, risk management, and other governance-focused roles.
Show More
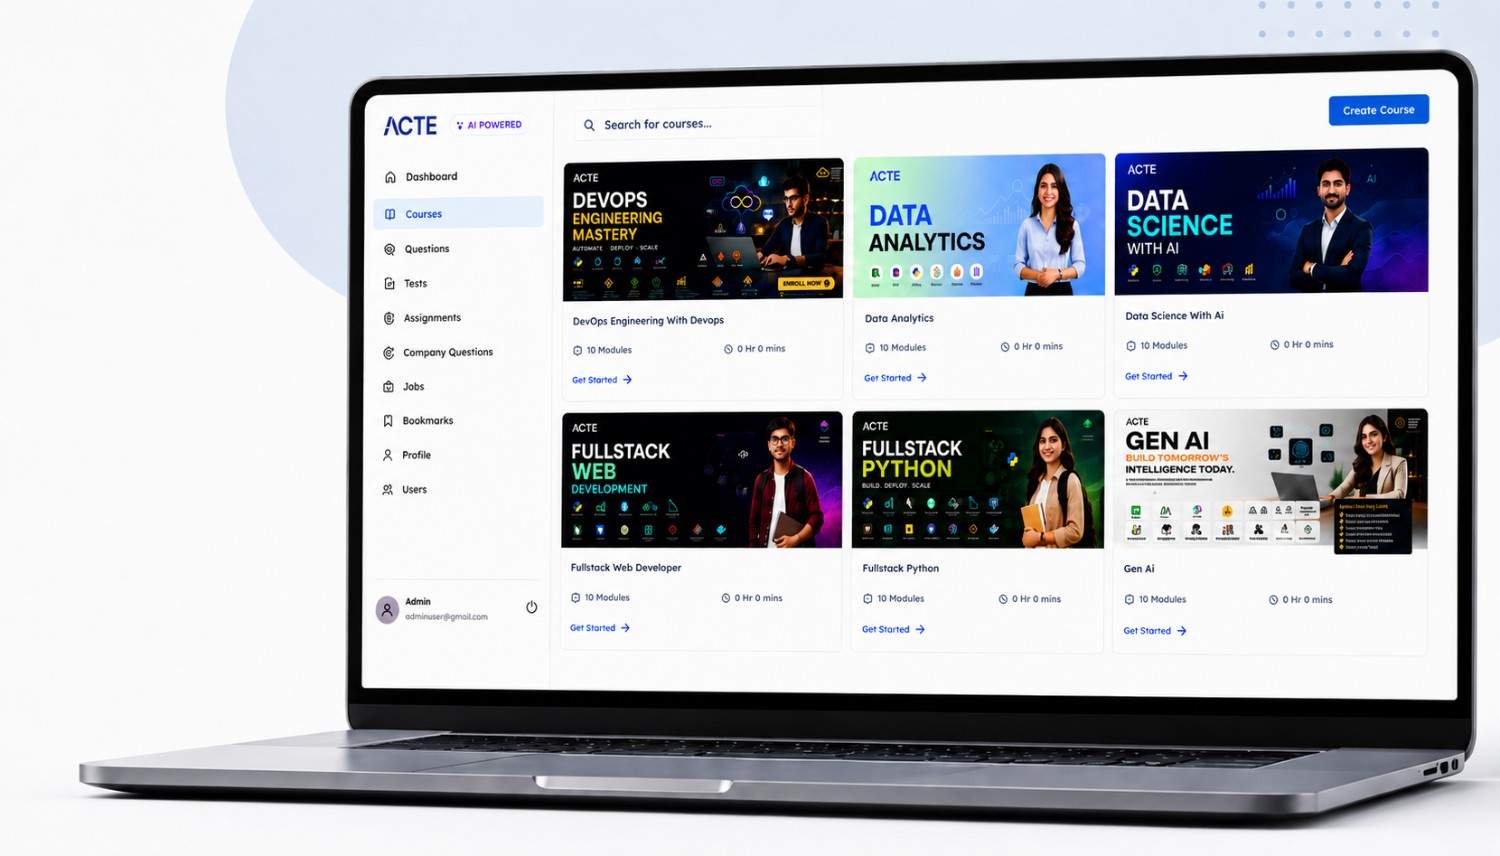
 LMS